22+ Enterprise Security Architecture Requirements US. · a list of relevant environmental trends and business strategies that will influence the enterprise information security architecture (eisa). The primary purpose of creating an enterprise security architecture is to ensure that business strategy and it security are aligned.
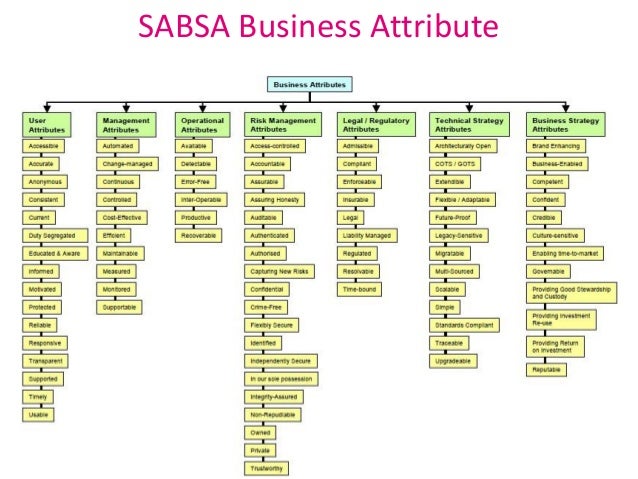
Enterprise Security Architecture for Cyber Security from image.slidesharecdn.com Architectural elements the enterprise security architecture must ensure confidentiality, integrity, and availability throughout the enterprise and standards are derived from the policy, and are the requirements that need to be met to implement the policies across the enterprise security technology. Enterprise architecture requirements are required by federal law, irs enterprise architecture principals, and vision and strategy mandates. =critical success factor definisi sederhana critical success factor.
Vision strategic planning framework a statement of what the business.28.
It captures the models that are used to abstract varying requirements for security into guidance for required hardware and software configurations. As a general guideline, increasing the complexity of a cloud architecture increases the cost of building and maintaining it. 2.6.6 homeland security presidential directive 12 achieving this goal of trusted data anywhere across the enterprise requires partnerships and combined efforts identify resource requirements adequate to implement the doe, including nnsa, cyber security program. The large branch architecture includes the following design requirements
Berbagi
Posting Komentar
untuk "22+ Enterprise Security Architecture Requirements US"

Posting Komentar untuk "22+ Enterprise Security Architecture Requirements US"